Service 04
Cloud infrastructure on Google Cloud.
We design, deploy and run the infrastructure under your product on Google Cloud: Cloud Run services and jobs, Cloud SQL and BigQuery, least-privilege IAM, CI/CD with Cloud Build, and monitoring with alert policies. AWS or Vercel when the product calls for them.
The problem
Production is a different job.
Code that works on a laptop still has to run somewhere: scheduled jobs that must run once, secrets that must not leak, databases only the right service can reach, deploys that must not break the release.
We design that part with the product, and keep it running. FundReachr, DataSync, and this website run on it.
What we build
Built for production from day one.
Cloud Run architecture
Cloud Run services and jobs, Cloud Functions, Cloud Tasks, and Cloud Scheduler: private, IAM-only workers called with OIDC tokens, and queues paced to their consumer (Cloud Tasks, chosen over Pub/Sub in an architecture decision record).
Databases and data
Cloud SQL Postgres behind a PgBouncer VM on a private VPC, IAM-authenticated database access through proxy sidecars, and BigQuery for the warehouse.
Security and least privilege
Least-privilege IAM bindings, keyless access, Secret Manager with key rotation without redeploys, consoles behind Identity-Aware Proxy, and an insert-only database role for a public webhook.
CI/CD
Cloud Build pipelines for every deployable service, database migrations that run before each deploy so a failing one stops the release, and promotion from dev to staging to production.
Infrastructure as code
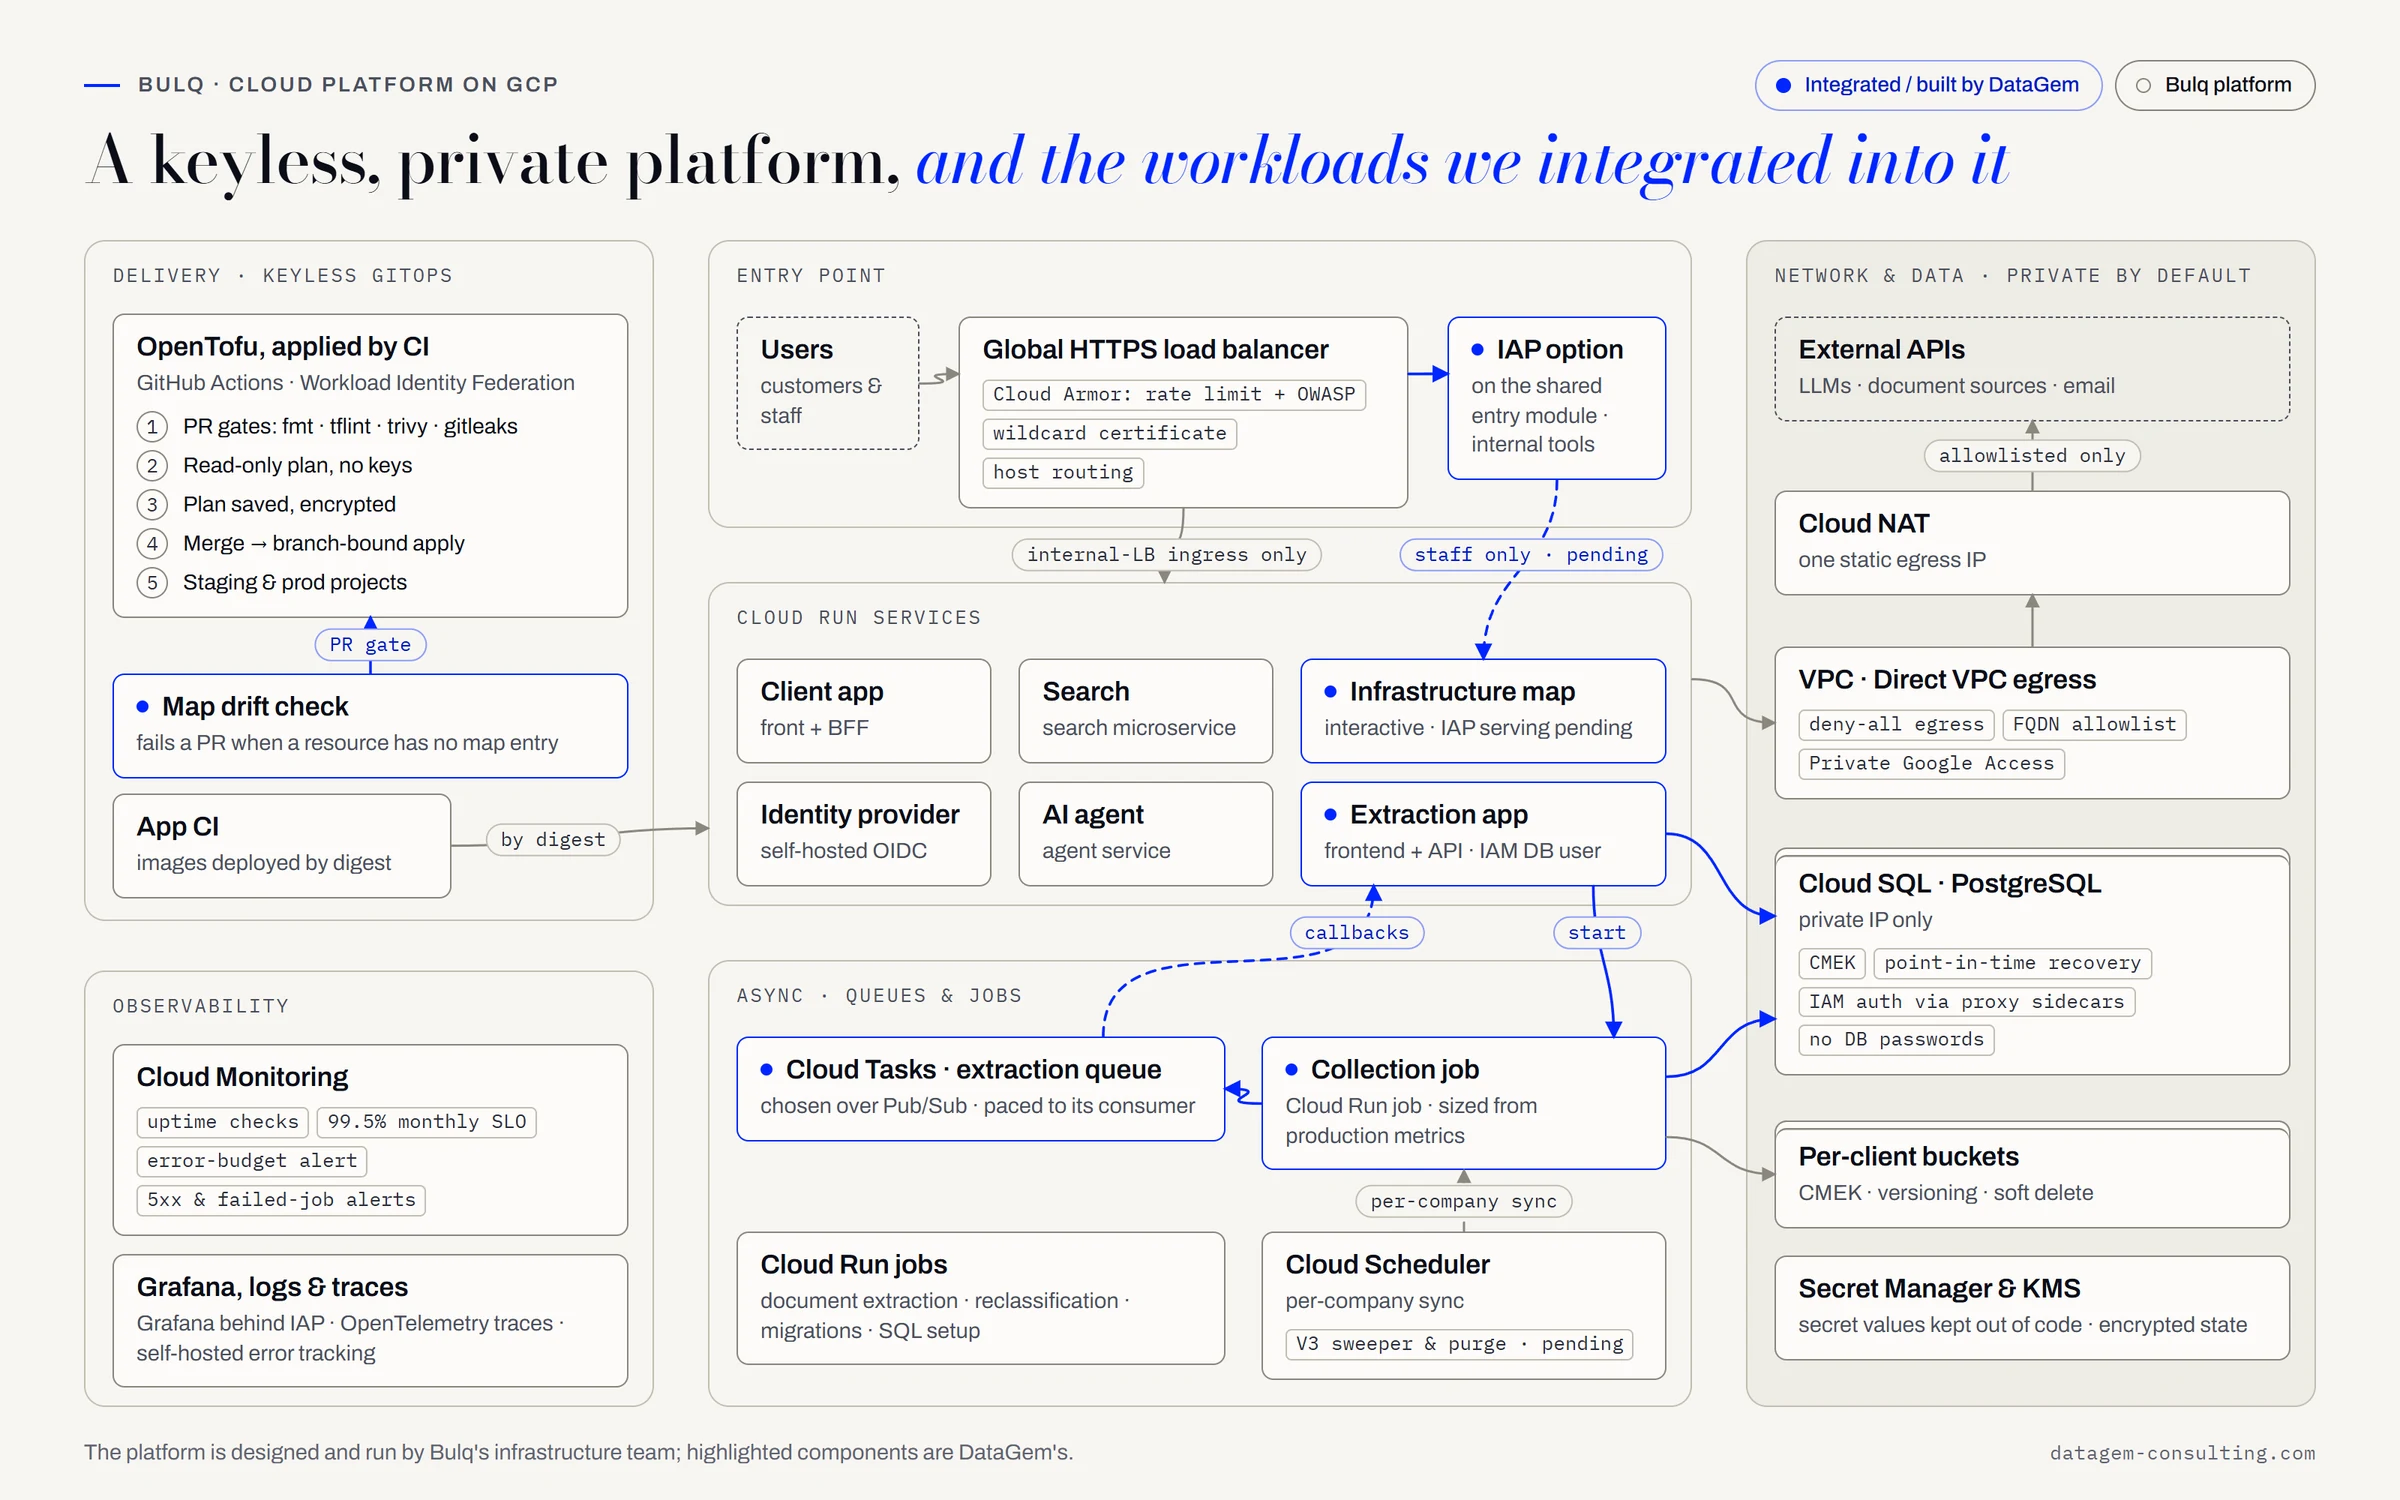
Workloads integrated into the staging environment of Bulq.ai's OpenTofu-managed platform, to its keyless, least-privilege standard, and an infrastructure map kept in step with the code by a CI drift check.
One project per client
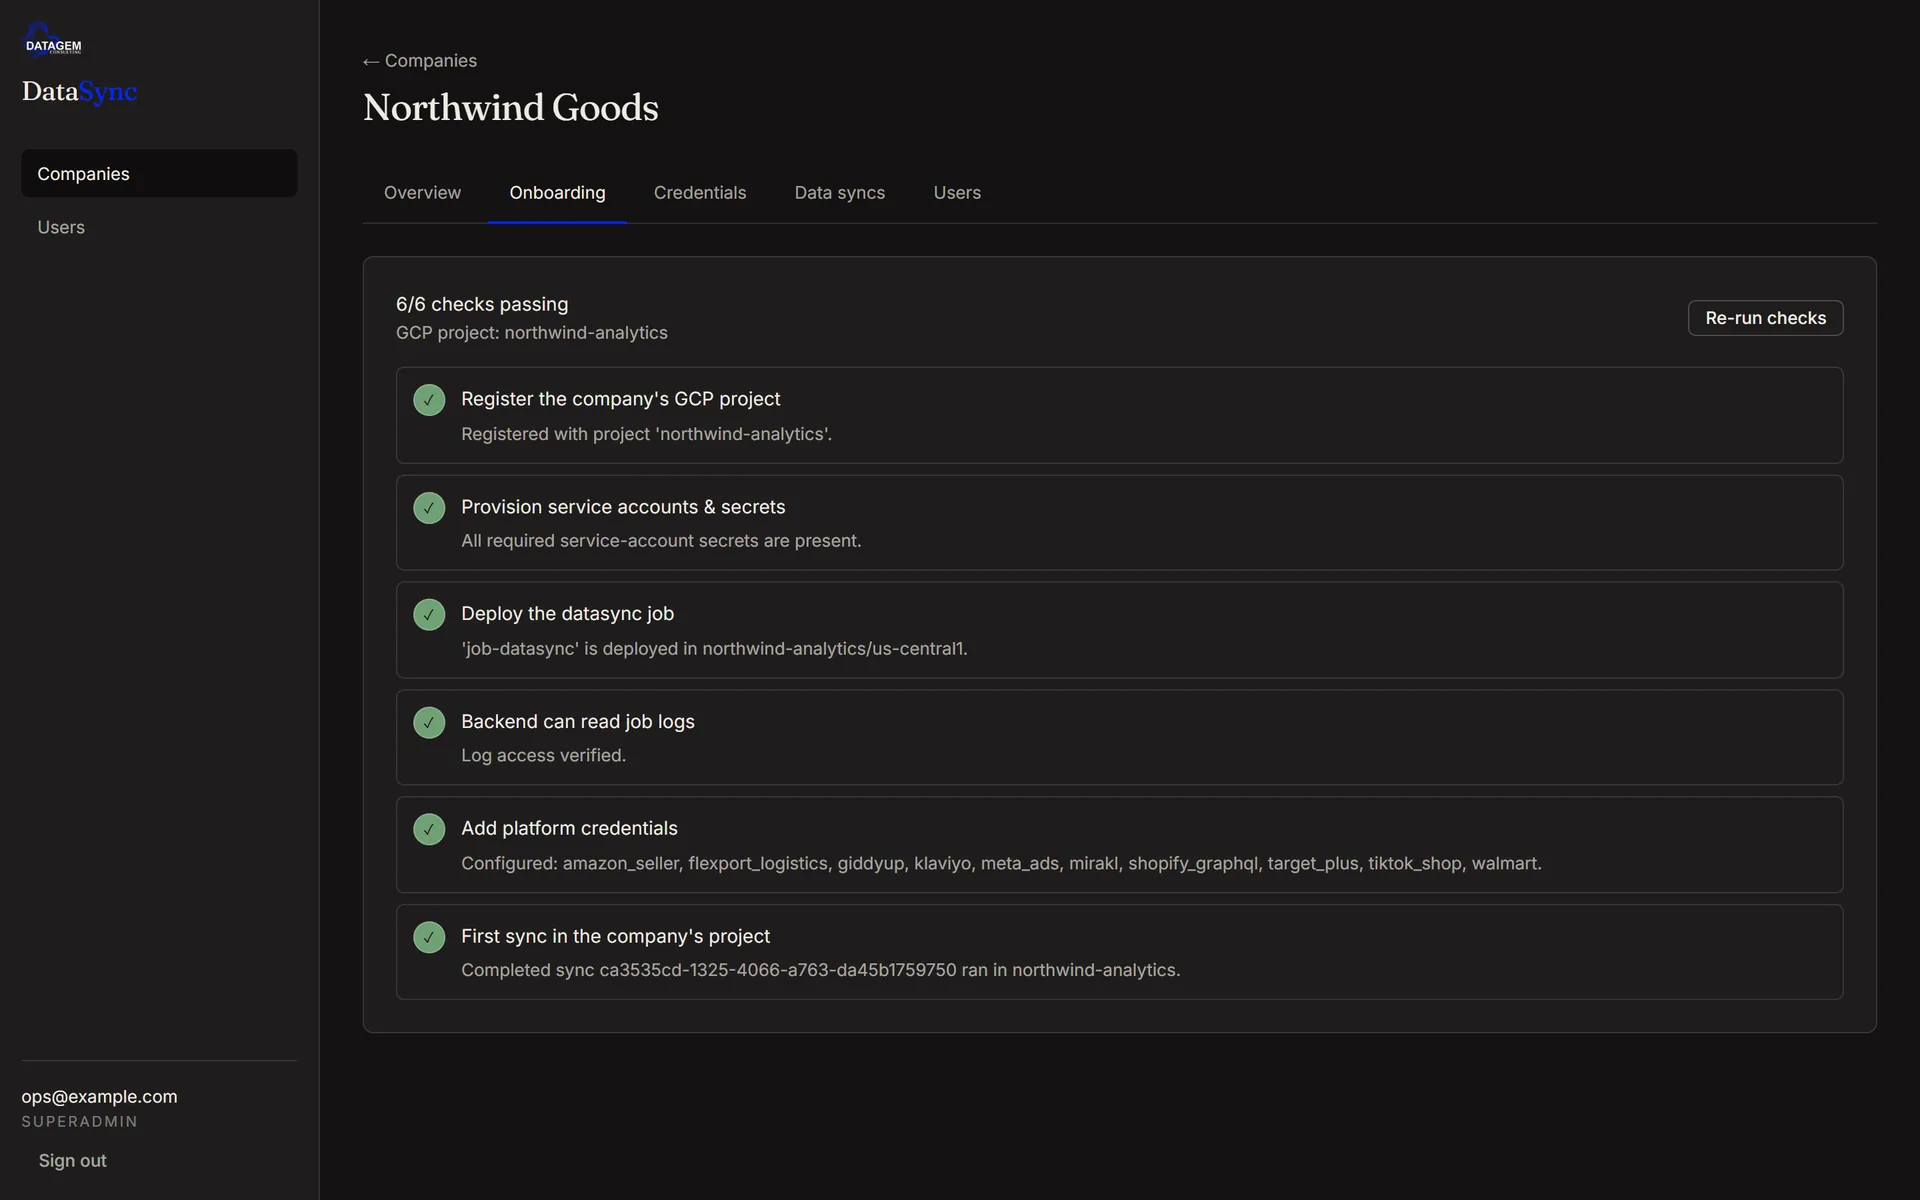
DataSync runs each client's syncs as Cloud Run jobs in the client's own GCP project, so compute is isolated and billed to the client, from one container image rolled out to every project.
Monitoring
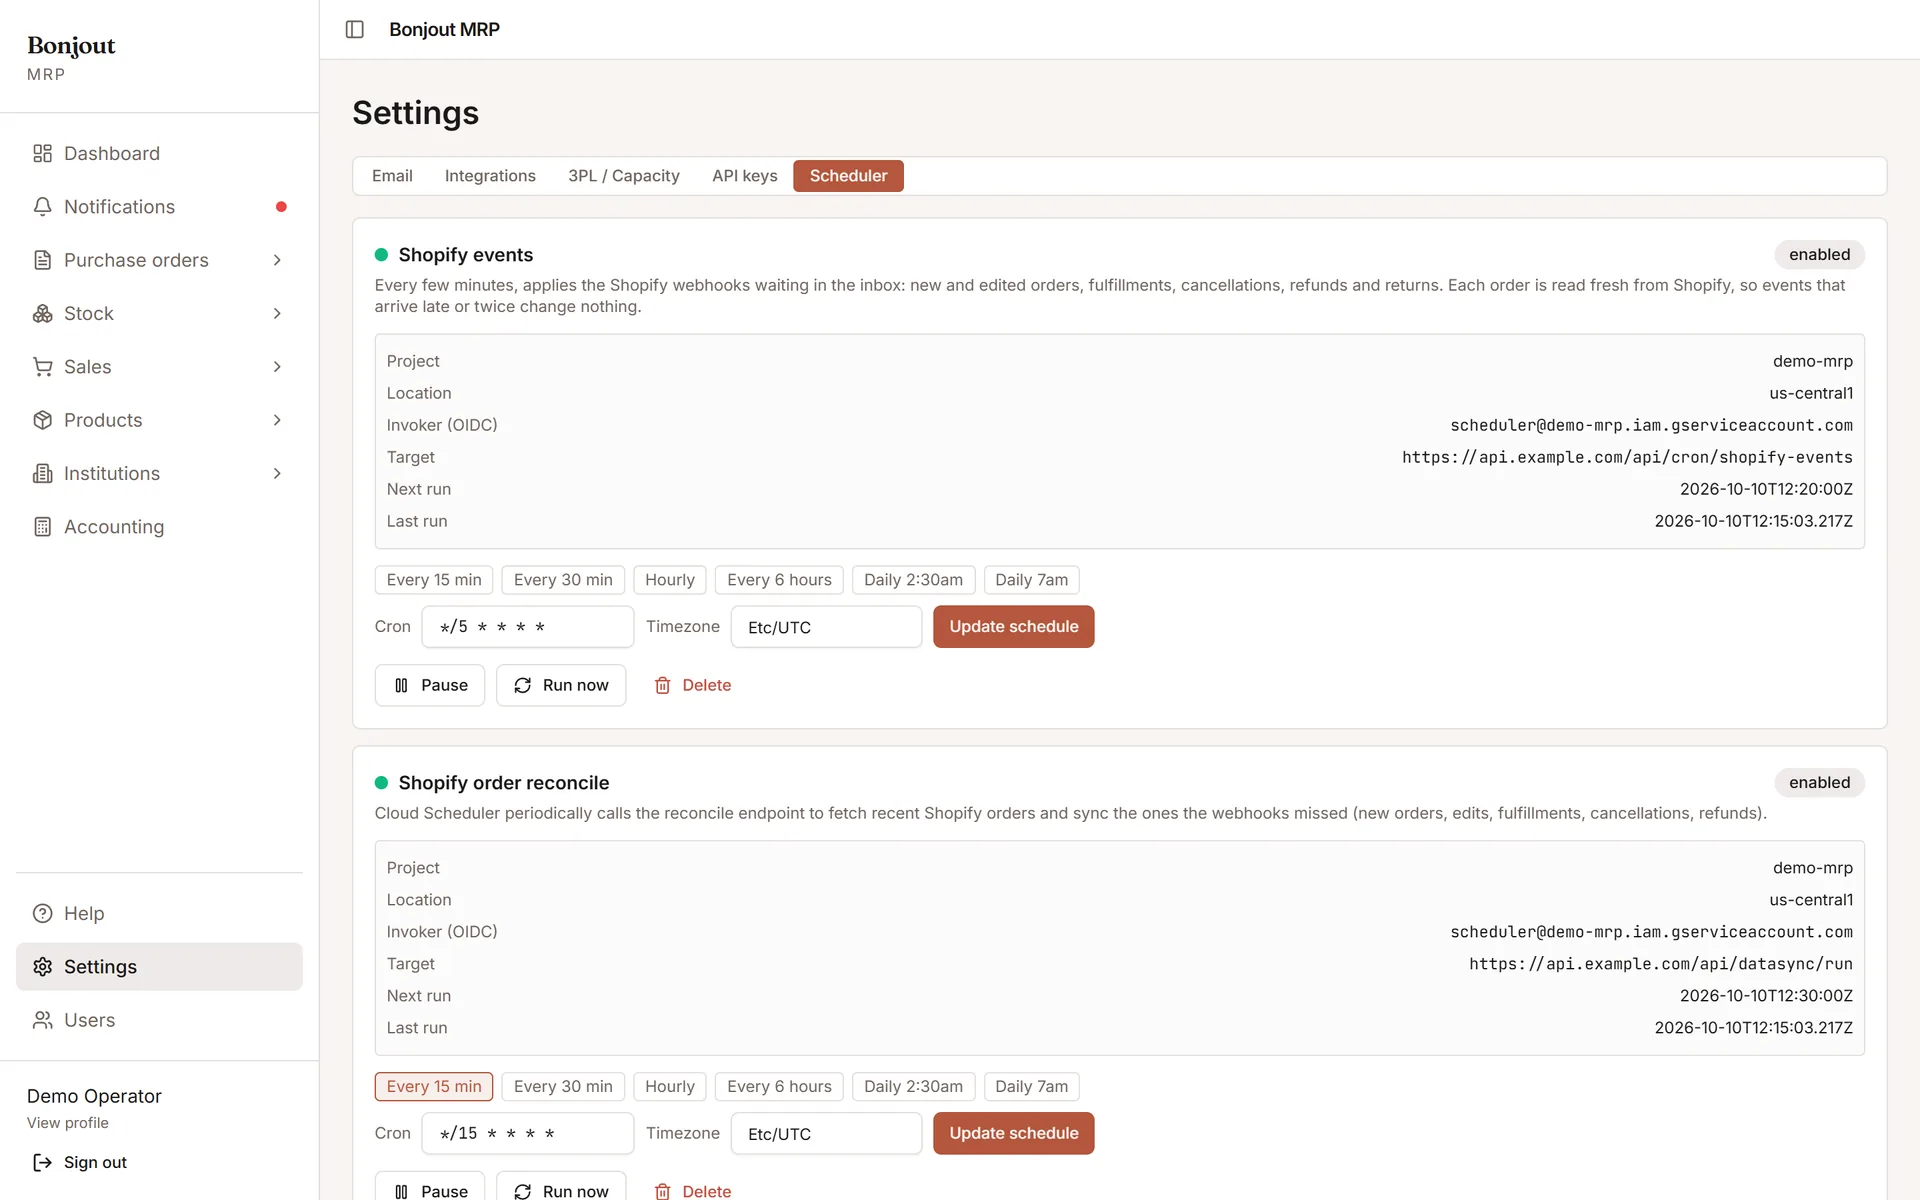
Cloud Monitoring alert policies, in-app alerts, live run logs, and OIDC-secured scheduled jobs managed from the app.
How we work
Designed with the product, run after launch.
01
Design it with the product
System architecture and interface, designed together so the product holds up in production.
02
Every deploy through a pipeline
At Purely White Deluxe, one Cloud Build pipeline provisions and deploys three Cloud Run services per app, and builds separate sandbox and production apps from the same code.
03
Your project, your bill
Workloads can run in your own Google Cloud project: Purely White Deluxe's integration is built that way, and DataSync runs each client's syncs in the client's project.
04
Run it
We deploy on GCP, AWS, or Vercel, then monitor and evolve what we ship.
Stack
Google Cloud, end to end.
Cloud Run, Cloud Functions, Cloud Tasks, and Cloud Scheduler; Cloud SQL and BigQuery; IAM, Secret Manager, and Identity-Aware Proxy; Cloud Build, Artifact Registry, and Cloud Monitoring; OpenTofu and GitHub Actions; nginx where a site needs it.
- Cloud Run
- Cloud SQL
- BigQuery
- Cloud Tasks
- Cloud Scheduler
- IAM
- Secret Manager
- Identity-Aware Proxy
- Cloud Build
- Cloud Monitoring
- OpenTofu
- nginx
Proof
Built on Google Cloud.
Construction · AI
Bulq.ai
From no-code to a real engineering platform
Bulq.ai's infrastructure team rebuilt its Google Cloud estate as OpenTofu code; DataGem integrated the extraction and data-collection workloads into its staging environment to the same keyless, least-privilege standard, and built an infrastructure map that a CI check keeps in step with the code.
Key figures
- Differently formatted supplier quotes
- Thousands
- LLM spend in the re‑architected pipeline
- Capped
- Recovery sweep in the re‑architected pipeline
- 5 min
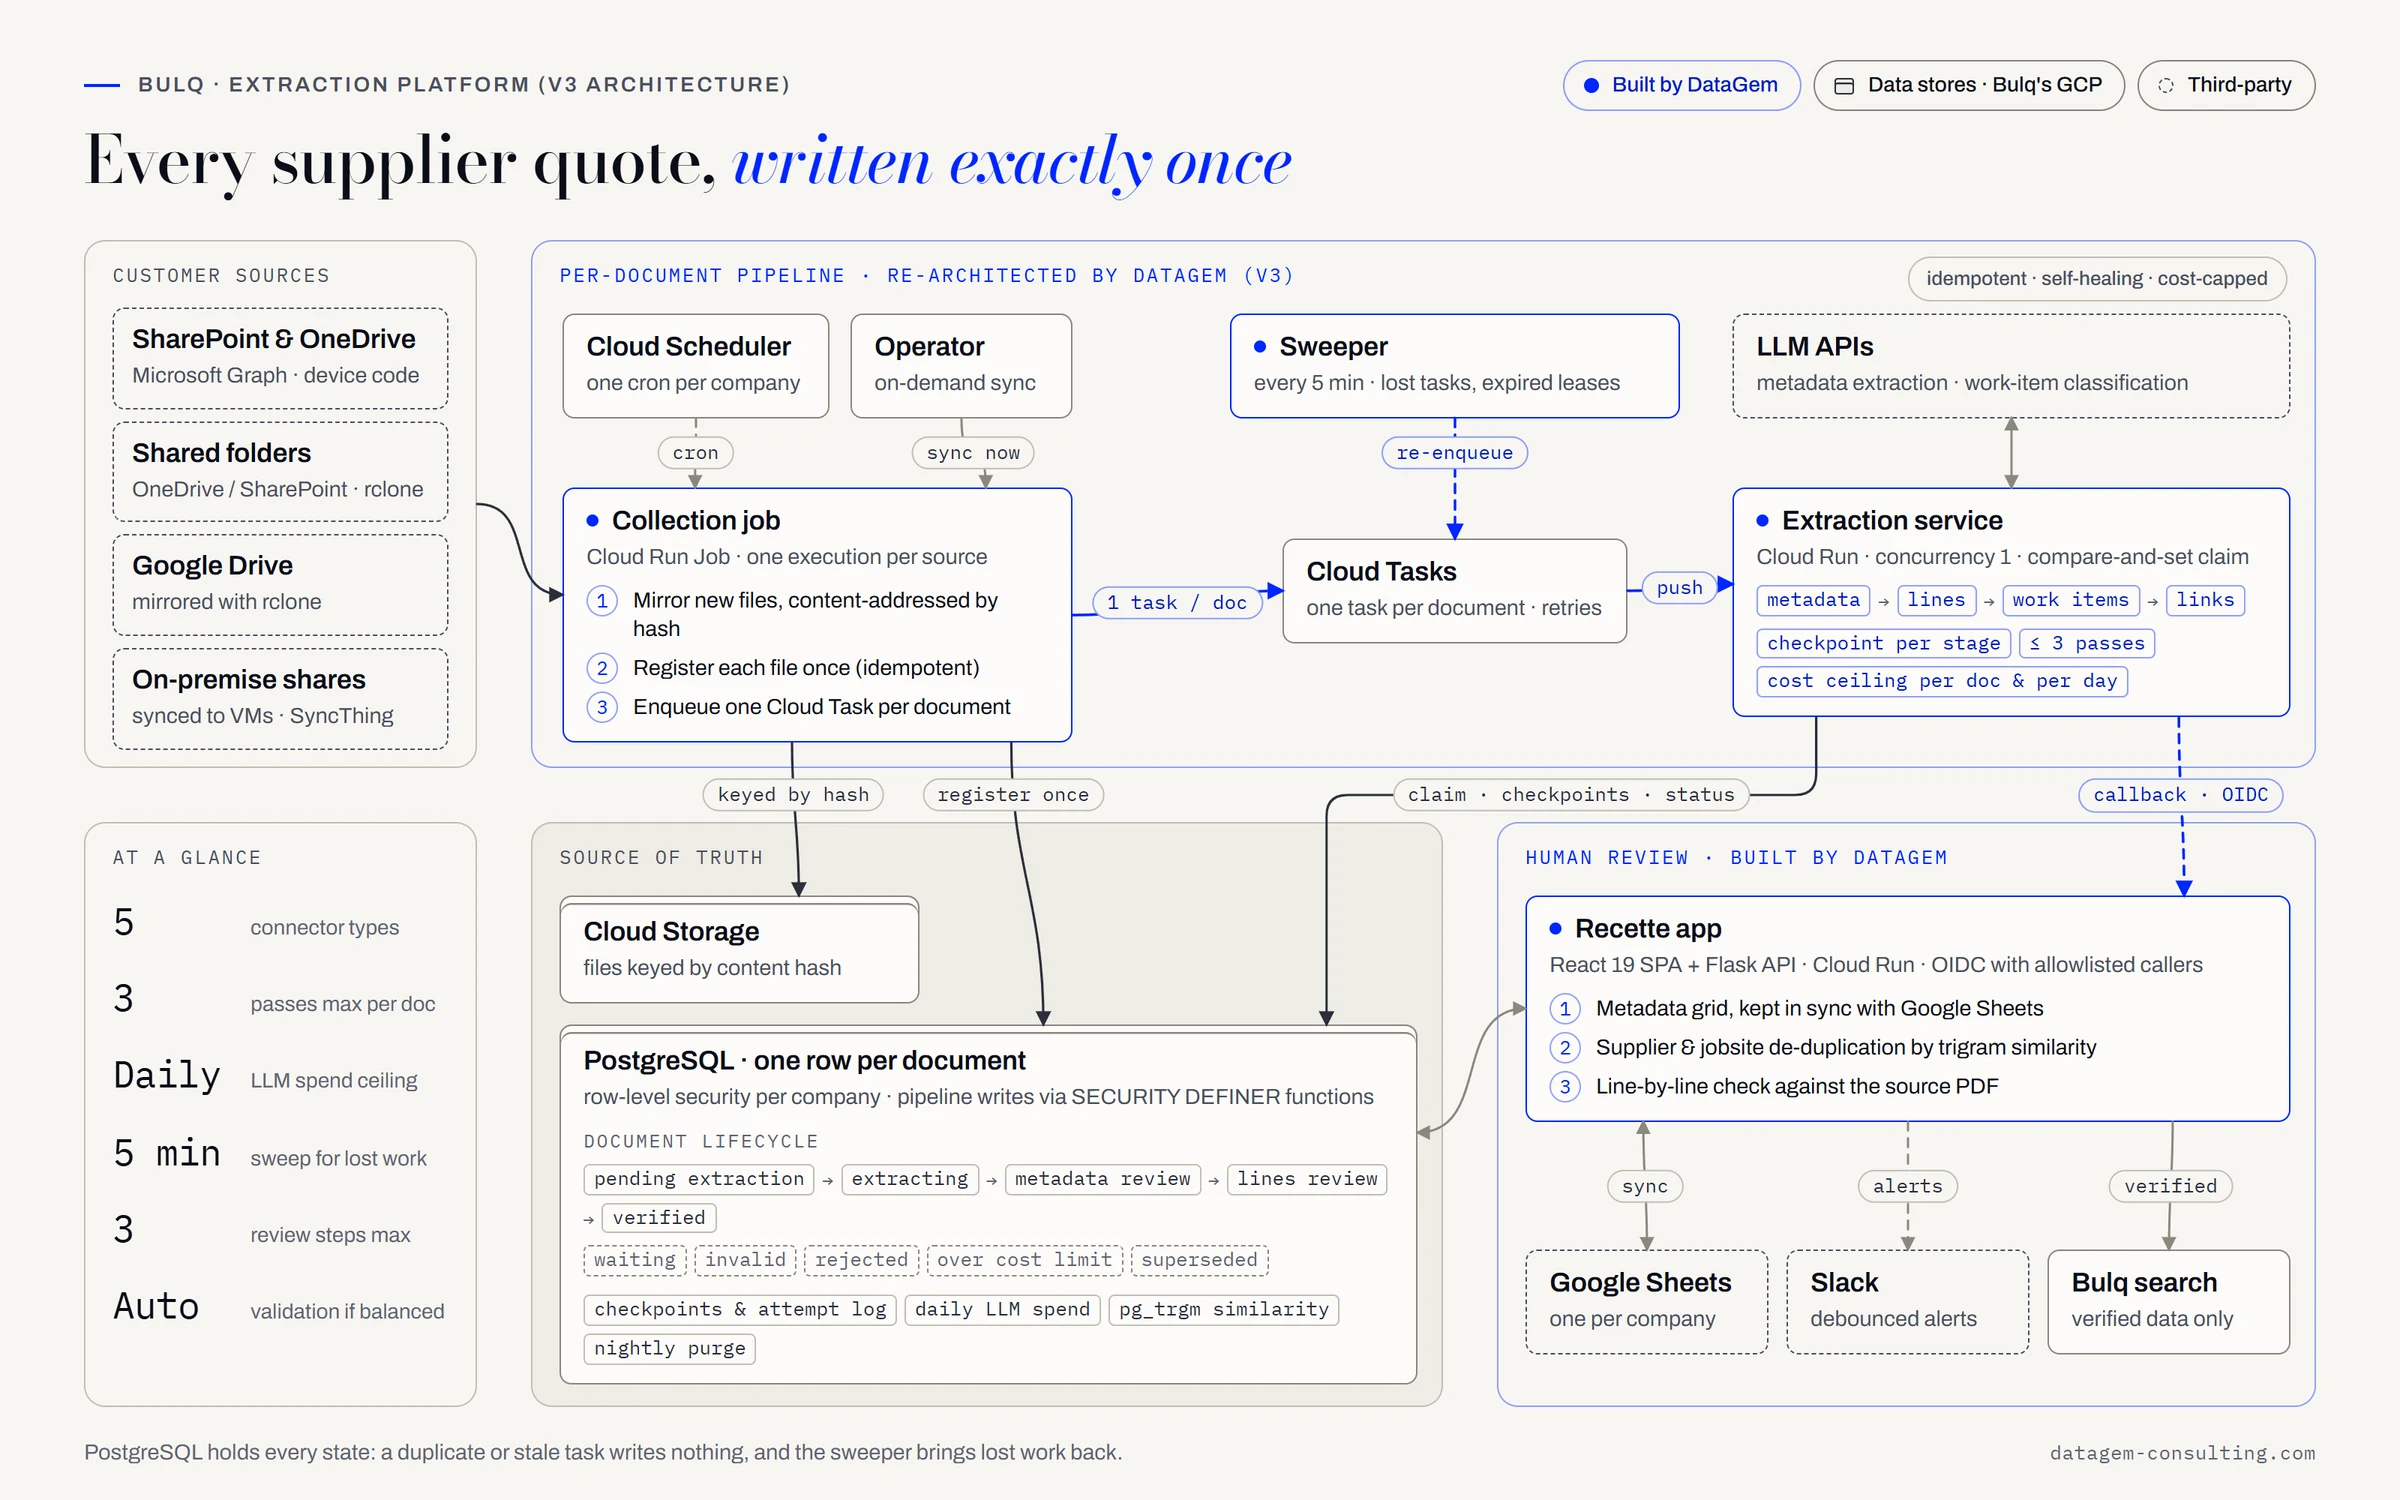
The V3 pipeline: one queued task per document, PostgreSQL as the single source of truth. Oral care · Marketplaces
Purely White Deluxe
Target Plus, wired straight into Shopify and Flexport
Built in the brand's own Google Cloud: three Cloud Run services per app (a console behind Identity-Aware Proxy, IAM-only jobs, a public webhook receiver), Cloud SQL behind PgBouncer on a private VPC, and one pipeline for sandbox and production.
Key figures
- Target polled for new orders
- 5 min
- Reconcile as a safety net
- 15 min
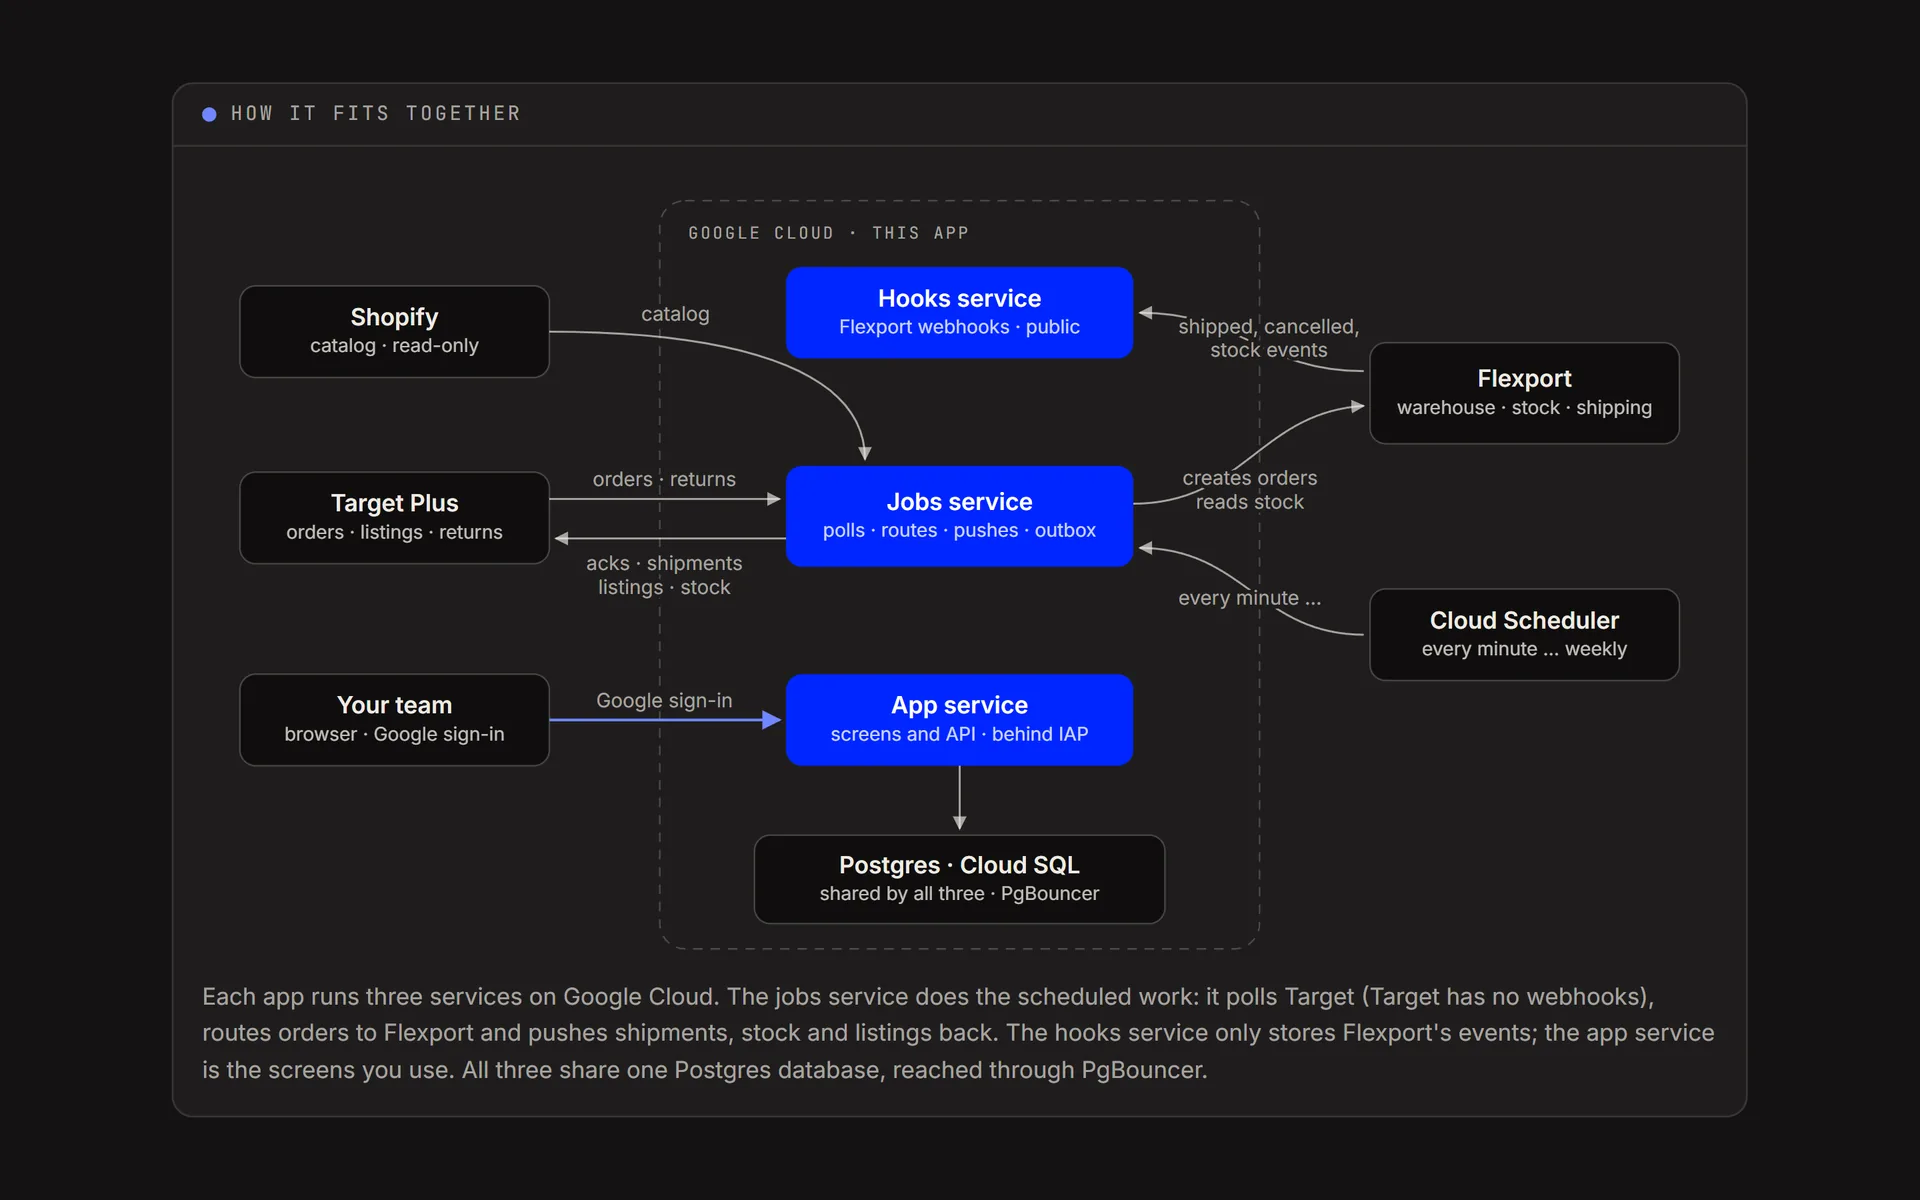
In-app help: how Shopify, Target Plus, Flexport and the three services fit together. Demo data CPG · Personal care
Bravo Sierra
Every data source, one dashboard
Bravo Sierra's syncs run on DataSync, which runs every client's syncs as Cloud Run jobs in that client's own GCP project, scheduled per connector over OIDC, from one container image.
Key figures
- Warehouse for DTC, wholesale and ad data
- 1
- Source platforms DataSync connects
- 19
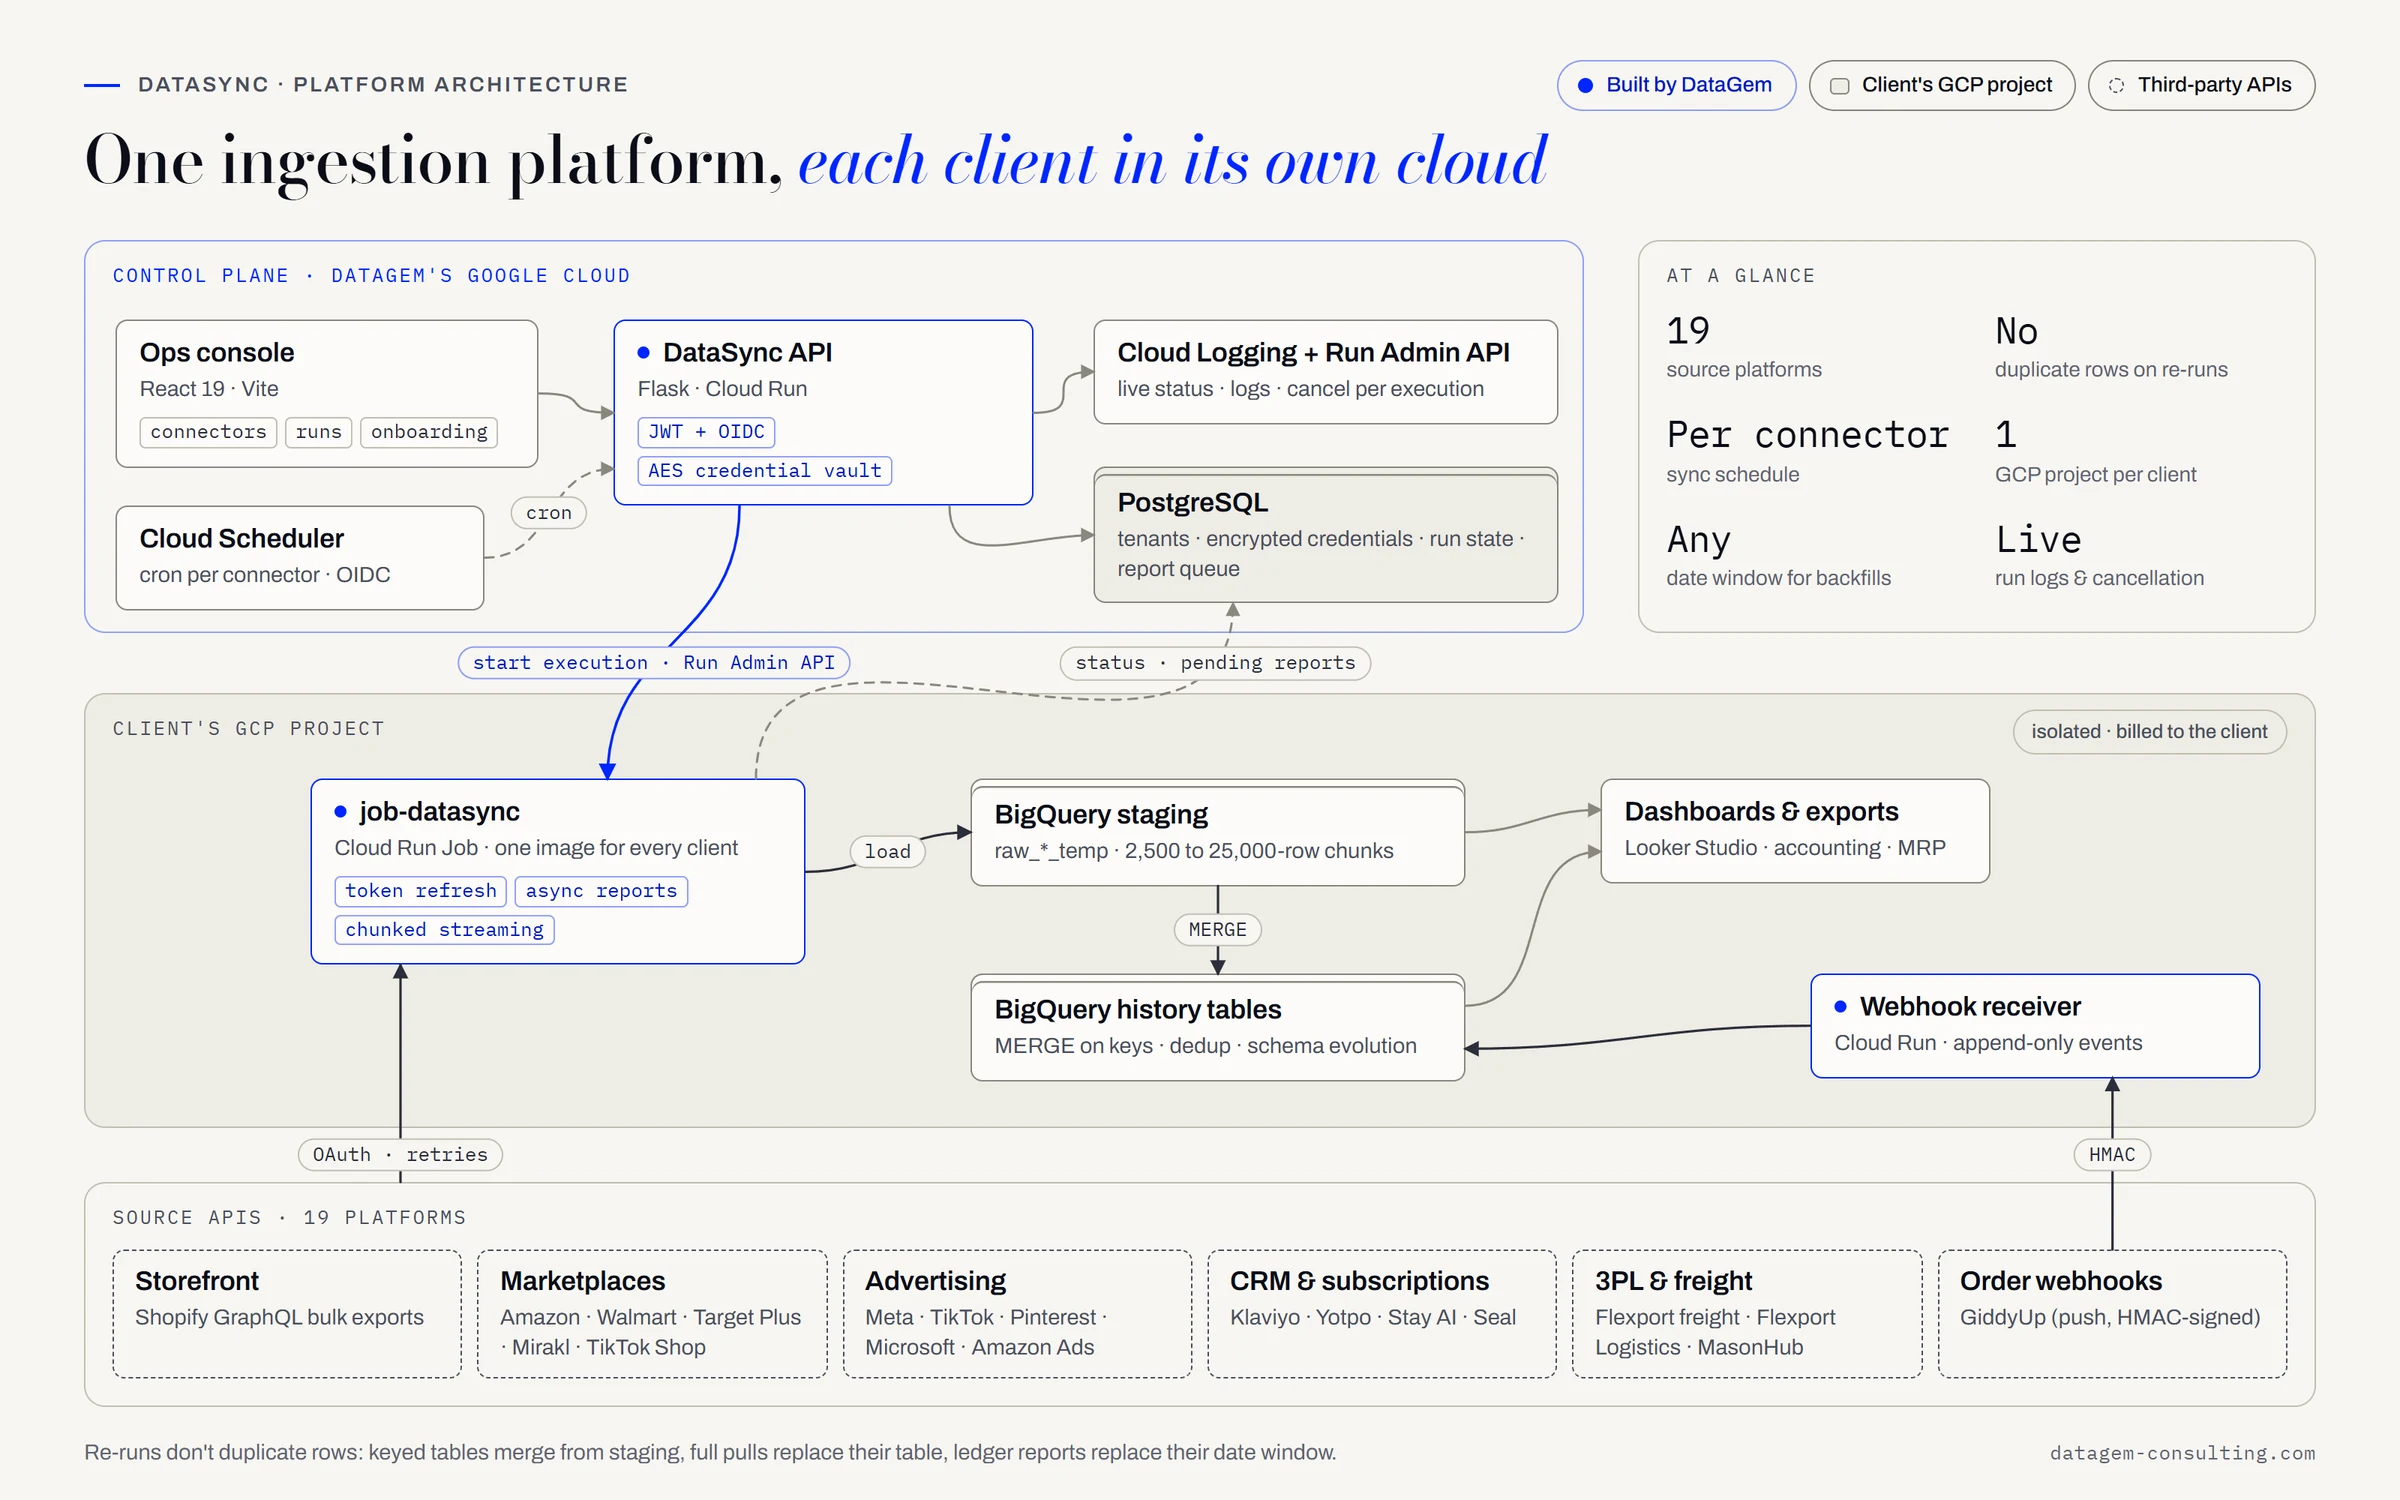
DataSync: one ingestion platform, each client in its own cloud. Software studio · Website
DataGem
This website, redesigned and rebuilt around the logo's own lines
This website: pre-rendered pages served by nginx on Cloud Run, built and deployed by Cloud Build on every push to main, with real 404s, long-term caching, and security headers.
Key figures
- Lighthouse performance score on desktop
- 100
- Layout shift as pages load
- 0
- Compressed JavaScript to load a page, down from 440 kB
- 130 kB
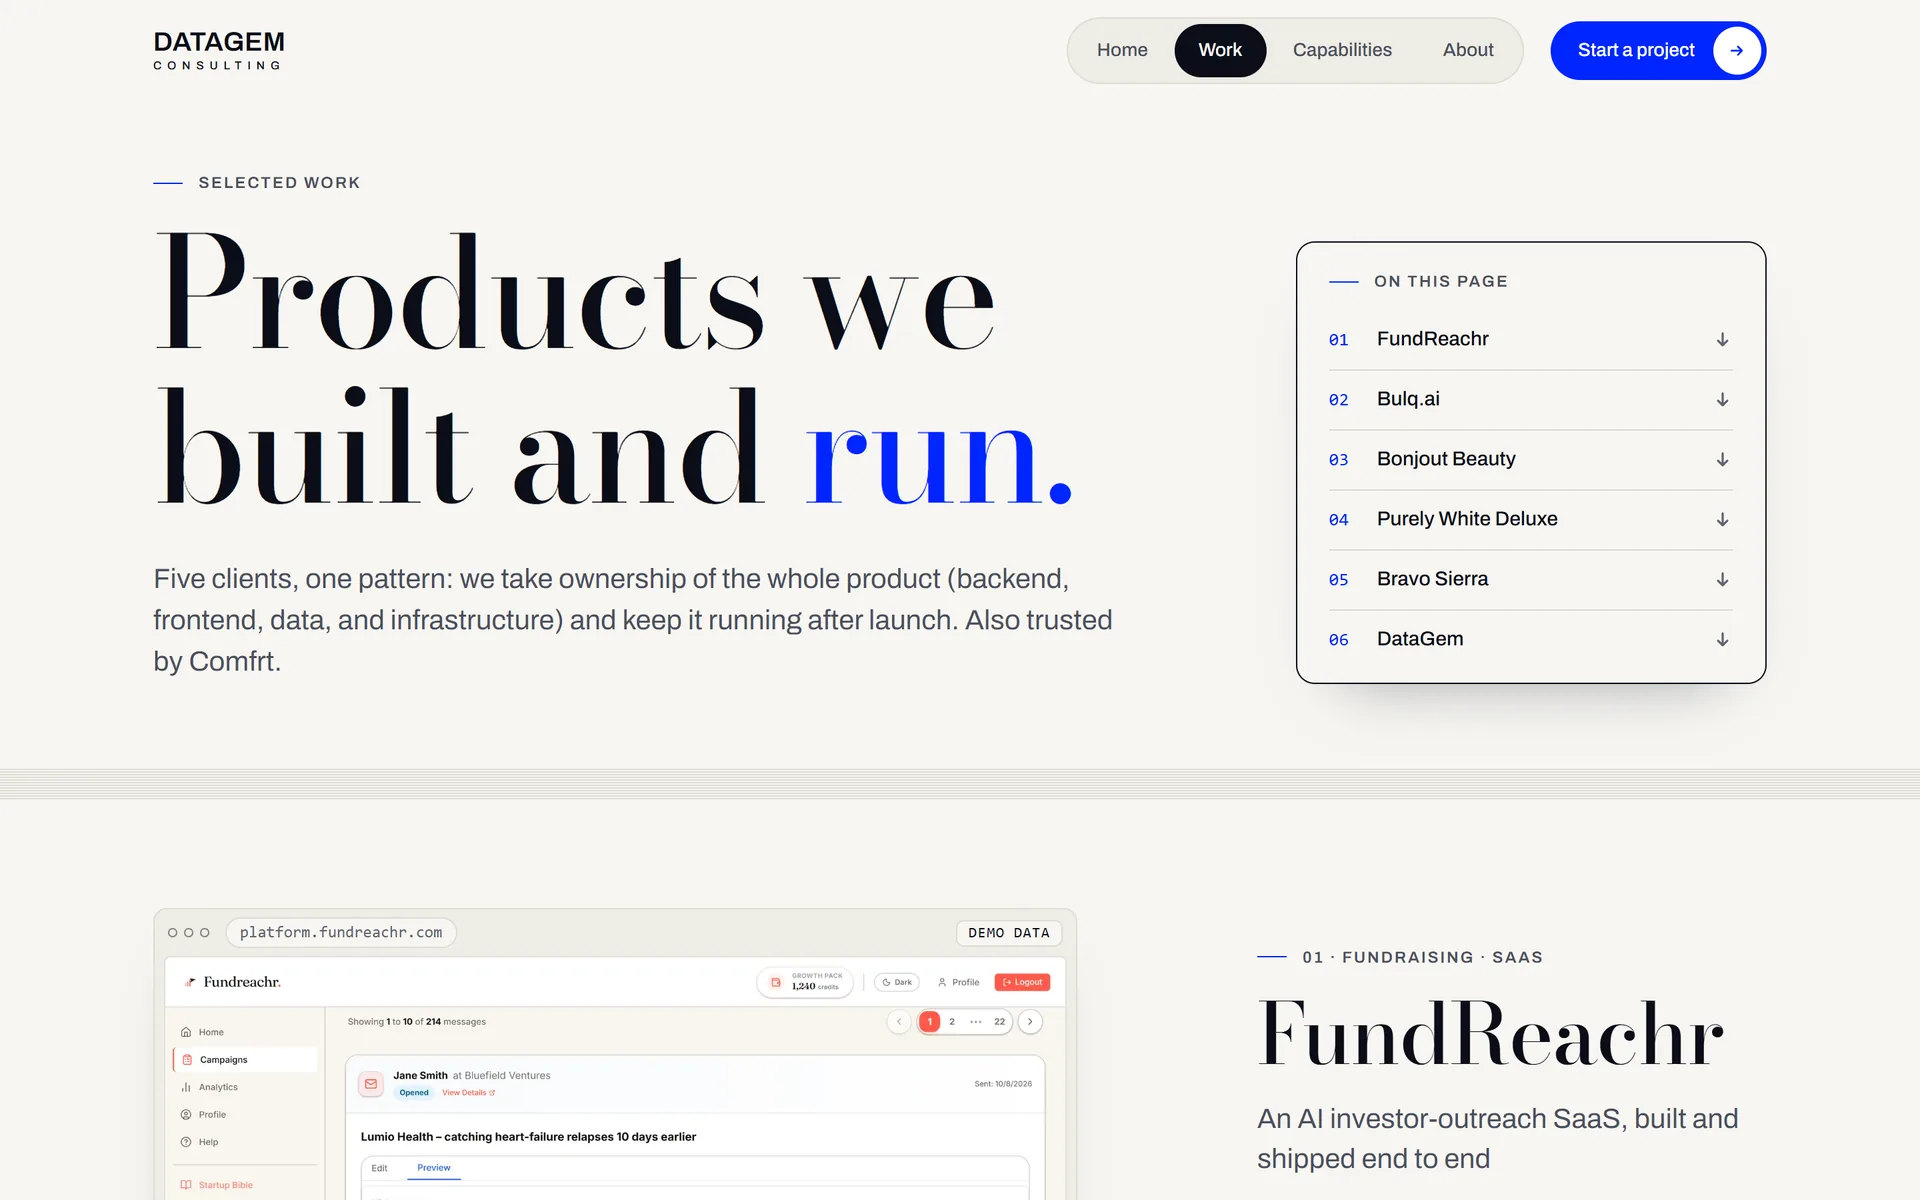
/work: the case studies and their index, pre-rendered from the same data that generates the routes and the sitemap.
FAQ
Questions, answered.
Do you work as a Google Cloud consultant on existing projects?
Yes. On Bulq.ai's platform, we integrated our workloads into the staging environment of the client's OpenTofu-managed Google Cloud, to its own keyless, least-privilege standard.
Why Cloud Run?
Cloud Run runs containers as services or jobs with no servers to manage, kept private behind IAM when they should be. FundReachr, Bonjout Beauty's MRP, DataSync, and this website run on it.
Can it run in our own Google Cloud project?
Yes. Purely White Deluxe's integration is built in the brand's own Google Cloud, and DataSync runs each client's syncs in the client's own GCP project, isolated and billed to the client.
How do you keep secrets and access safe?
Least-privilege IAM, keyless access where the platform allows it, secrets in Secret Manager rotated without redeploys, OIDC tokens on scheduled and queued calls, and private services reachable only through IAM or Identity-Aware Proxy.
How do deploys work?
Through Cloud Build: every deployable service has its own pipeline, database migrations run before the API deploys so a failing one stops the release, and changes move from dev to staging to production.
Do you only work on Google Cloud?
Our case studies are built on Google Cloud, and we also deploy on AWS or Vercel when a product calls for it.